Press Release · Anyday Security
Anyday Security Launches ExploitTotal to Provide Defenders Free AI-Built Working Exploits in Minutes from Patch Release
Distributed by TenNet Team · Originally issued via PR Newswire
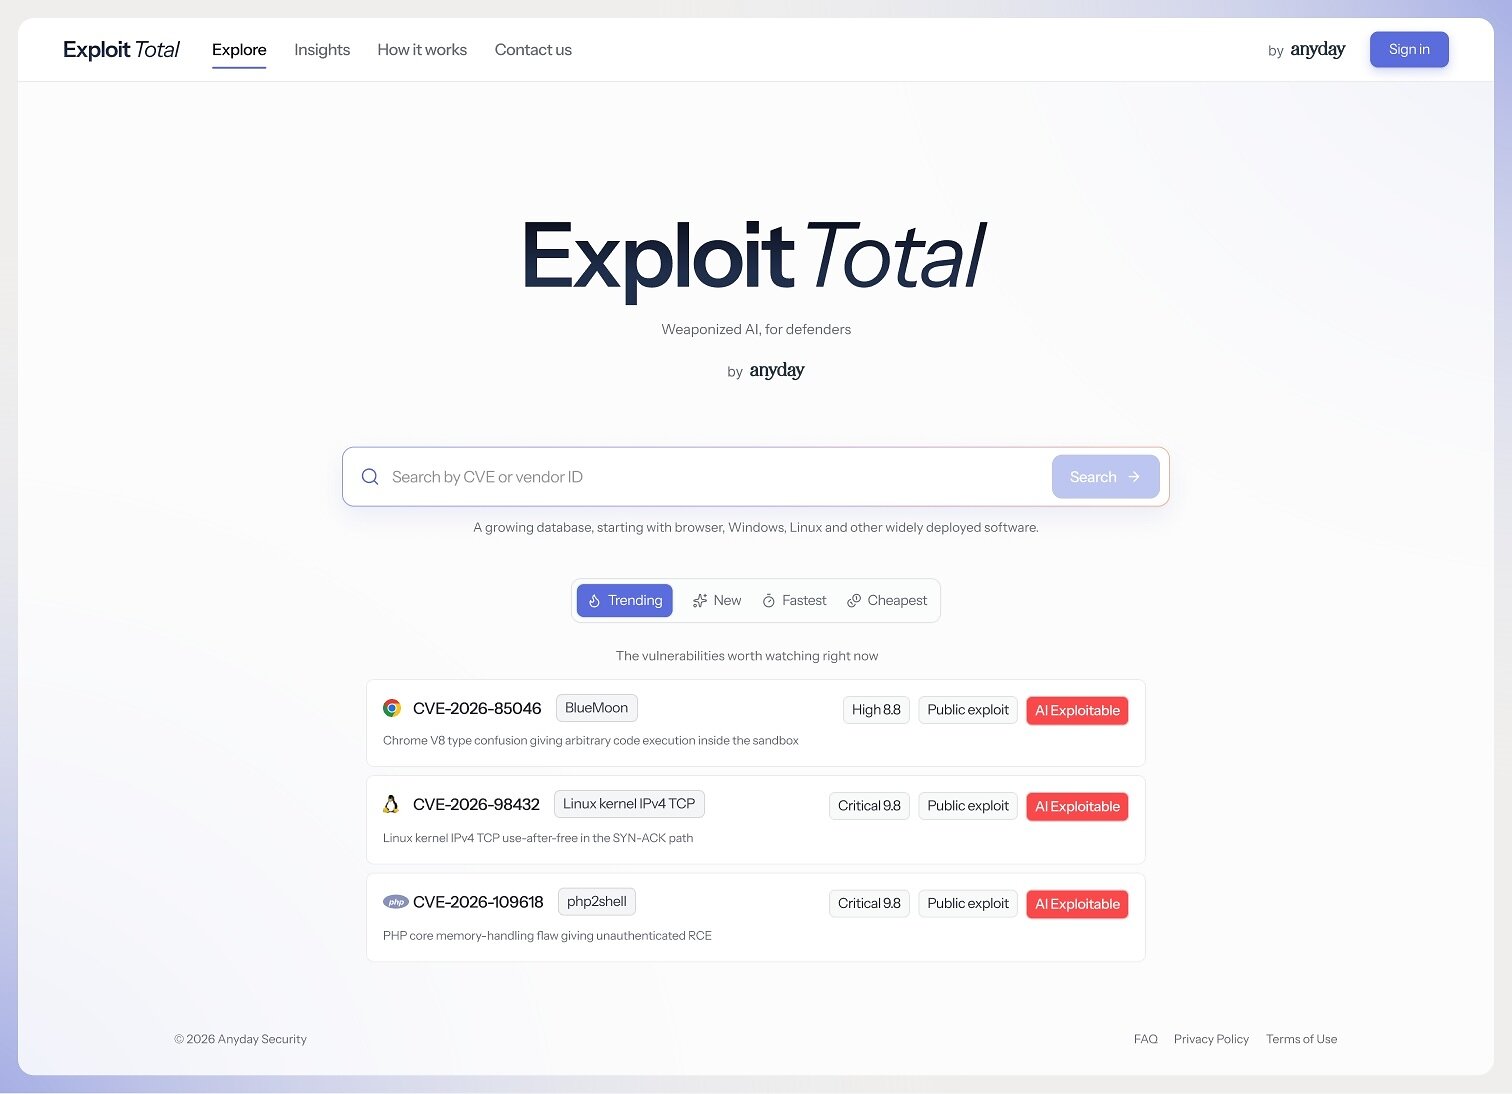
ExploitTotal.ai already contains 200+ working AI-generated exploits on the platform, including 70%+ for vulnerabilities with no known working exploit Proof of Concept (PoC)
NEW YORK, Nov. 11, 2026 — Anyday Security, a start-up building the defense layer for the age of AI-powered adversaries, today launches ExploitTotal.ai, a free platform that shows defenders which vulnerabilities open-weight AI models can readily exploit, and gives security professionals validated, compliant, actionable PoCs for free, so they can test whether they are exposed and build detection rules.
Turning a patch into a working attack was once slow, specialist work. According to Anthropic, frontier AI models can now build a working exploit within an hour of a patch's release, and that capability is no longer limited to tightly controlled models. GLM-5.3, which the U.S. government's Center for AI Standards and Innovation called the most cyber-capable open-weight model to date, builds exploits end to end and was released without meaningful safeguards, which researchers bypassed between 64% and 100% of the time.
Recent major security incidents such as PHP2Shell, where attackers tried to exploit flaws before a patch was released, show that offensive AI exploitation is no longer theoretical. Security teams need to react faster.
"AI has collapsed the distance between a vulnerability and an exploit," said Yonatan Gorfung, CEO and Co-Founder of Anyday Security. "For 20 years, 'no public exploit' meant the exploit most likely didn't exist. Today it only means nobody has published one. Delivering an exploit used to take a nation-state or elite researchers weeks. Now anyone with a free open-weights AI model can do it in minutes, for less than the price of a coffee, and threat actors are doing exactly that. We built ExploitTotal, so defenders get these exploits first and gain an edge over cybercriminals."
Microsoft fixed 1,411 vulnerabilities in its October 2026 Patch Tuesday, more than in all of 2025. Yet, according to Verizon's 2026 Data Breach Investigations Report, organizations took a median of 43 days to remediate actively exploited vulnerabilities and fully remediated only 26% of them. Meanwhile, exploitation is surging, with Google Threat Intelligence Group reporting an average of 18 exploits per month in 2026, nearly double 2025's number.
Anyday Security uses the same models AI attackers do. It gave GLM-5.3 200+ known vulnerabilities, including some of security's hardest targets in widely used browsers and operating systems, with only what any attacker has the day a fix is announced; the vendor's public description of the vulnerability and the patch itself. Anyday then checked every successful exploit against the U.S. National Vulnerability Database, CISA's catalog of known exploited vulnerabilities and public exploit repositories and found that 72% had never had a public exploit. In one demonstration, the model built a complete full-chain, working browser exploit in minutes for less than a dollar.
"A security team knows of thousands of vulnerabilities in its environment but has a working exploit for almost none of them," said Omri Sibony, Co-Founder and CTO of Anyday Security. "Our system produces exploits the same day a vendor releases its fix, so a team can look up its own vulnerabilities, run the exploit against its systems and see whether its tools stop the attack. If not, it can write a detection rule or virtual patch against the real attack instead of finding out during a breach. Attackers have always moved first. We're helping security teams stay one step ahead."
Each vulnerability page on ExploitTotal.ai leads with a verdict on whether the AI models can weaponize the vulnerability, the cost and time to build the exploit and the model that produced the strongest result. Each exploit is graded on a five-level scale, from crashing the target program to taking full control of it. Pages also show severity and whether a public exploit exists, and every result is tagged with its model and date, so the catalog also tracks how fast AI exploit capability is advancing. Anyone can search the ExploitTotal.ai catalog for free. Signed-in users see the full AI exploitability assessment, and verified users can download unweaponized PoCs, which run against the vulnerable code without a harmful payload. All PoCs are designed for security teams' authorized testing, research and defense, and cover patched, publicly disclosed CVEs.
ExploitTotal.ai currently covers the most widely used software in enterprises - Windows, Linux, Chrome, Firefox and Edge etc, and Anyday Security updates the catalog continuously as its automated system runs and new AI models are released.
ExploitTotal.ai is available now for free at https://exploittotal.ai.
Media Contact
Hannah Yoken
[email protected]
SOURCE Anyday Security
About Anyday Security
Anyday Security is building the defense layer for the age of AI-powered adversaries, to prevent exploitation at scale. The company was founded by Israeli military's Unit 8200 veterans Yonatan Gorfung (CEO) and Omri Sibony (CTO), previously Director of Security Research at SentinelOne. The company has headquarters in New York and an R&D center in Tel Aviv. Learn more at https://anyday.security.